
Solana Foundation Requests Node Operators to Address Linux Kernel Vulnerability NoisyTCP

 Prefer us on Google


The Solana Foundation has issued a security notice, urging all node operators running the Agave or Firedancer clients to take immediate action regarding the Linux kernel vulnerability CVE-2026-99288 (NoisyTCP). Node operators should check the security announcements of their Linux distributions to confirm whether their current kernel is affected, and upgrade the kernel as soon as a fix is released. If a patch has not yet been released, SYN Cookies can be temporarily disabled without needing to restart the validating node. After starting the patched kernel, SYN Cookies should be restored to their original settings.
-- Price
This content is provided for general informational purposes only and doesn't constitute financial, investment, legal, or tax advice. Any events, rewards, online promotions, or related information mentioned herein should not be considered a recommendation, solicitation, or invitation to purchase, sell, trade, or otherwise deal in any crypto assets. Crypto assets are highly volatile and may result in loss. The availability of WEEX services, products, and related events may vary by region. You are responsible for ensuring that your participation is in accordance with applicable local laws and regulations.
You may also like

JPMorgan and MIT Map More Than 150 Requirements for Institutional Blockchains

Backpack Founder’s Latest Speech: Solana Will Become the API of American Finance, Welcoming the Era of Neobrokerage

NYSE Parent Company Considers Operating Solana Validators

Clarity Act Defeat ‘Failure of American Leadership’: Trump’s Former Crypto Chief

William Shatner disowns QUATS token and calls charity pitch a scam

Helius CEO emphasizes Solana privacy features for institutional adoption

'Tokenization Is Not the Finish Line': Jupiter to Let Users Borrow Against Bullish Shares
Solmate plans AI GPU service with Solana payments: What do we know?

Hong Kong Establishes Task Force to Support Cryptocurrency Declaration and Tax Registration

Boris Johnson: The UK Must Lead in Blockchain and Asset Tokenization

Corda Protocol EPIC Launches on Solana, Opening $2.5 Trillion Market

'Nobody Knows Who's in Charge': Boris Johnson Stands by Bitcoin Skepticism at Breakpoint

Kamino Launches Trading Execution Algorithm ONE and Institutional Platform Omni
Zelle Demonstrates $1.25 Million Crypto Transfer on Solana Devnet

Ledger Launches Clear Signing Feature on Solana, Supporting Jupiter and Kamino

Solflare brings USDC cash withdrawals to 170+ markets with MoneyGram

Matt Hougan has a positive outlook on Bitcoin and altcoins

Solana Breakpoint attendees warned of robberies after reported wallet theft

Solana Launches 1.0, Renames Mainnet to Mainnet

Thailand Proposes Daily Stablecoin Transfer Cap for Regulated Platforms
CoW Swap Launches on Solana, Supporting USDC and Wrapped SOL Exchange

CoW Swap Launches Alpha Version, Supporting USDC and wSOL Exchange
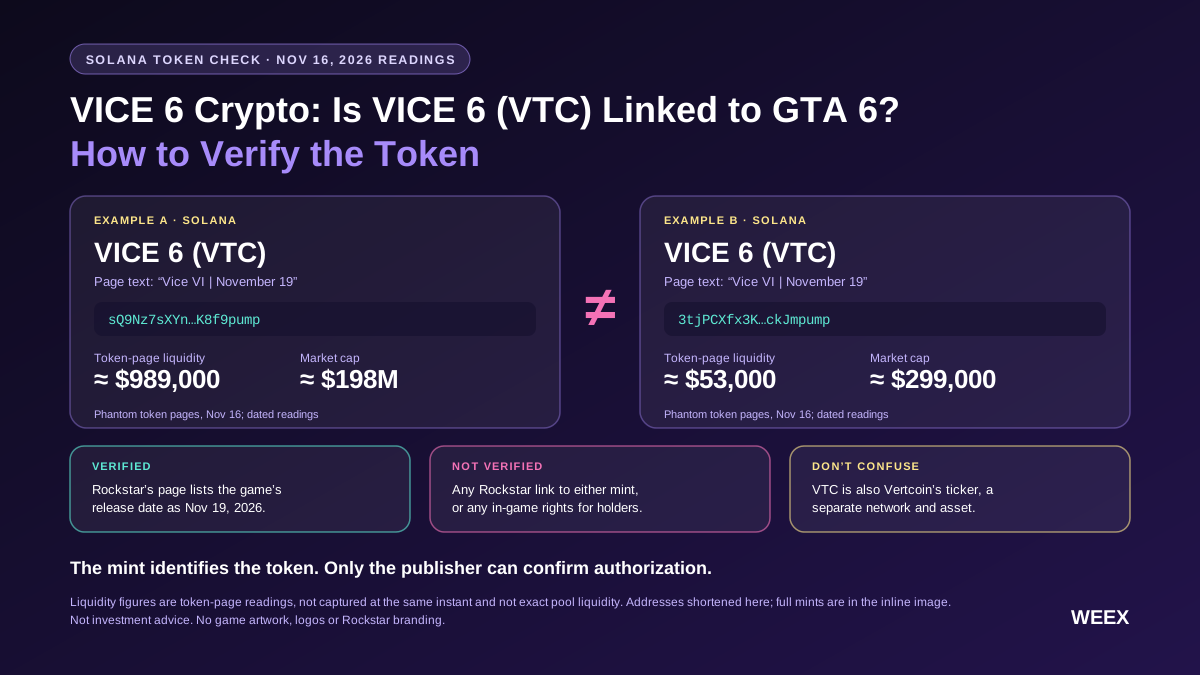
VICE 6 Crypto: Is VICE 6 (VTC) Linked to GTA 6? How to Verify the Token
Is VICE 6 crypto linked to GTA 6? Compare two Solana tokens using VTC, verify their mint and pool addresses, and see what Rockstar has confirmed.

Harvard and Dartmouth Bitcoin ETF Holdings Remain Unchanged in Q3

Morgan Stanley Q3 Holdings: Nvidia and Apple Continue to 'Anchor', Increasing Investment in AI Supply Chain, Establishing Position in SK Hynix

DTCC Plans to Introduce Tokenized Securities and Bonds on Solana by 2027—Expanding Under Wallet Restrictions

Wattenhofer and Kniep Join Solana Foundation
Stablecoin Supply Shrinkage Raises a Bigger Question About Crypto Liquidity
21 Banks Commit $270 Million to Project Faro

How Wall Street Is Racing to Claim the Onchain Dollar
JPMorgan and MIT Map More Than 150 Requirements for Institutional Blockchains
Backpack Founder’s Latest Speech: Solana Will Become the API of American Finance, Welcoming the Era of Neobrokerage
NYSE Parent Company Considers Operating Solana Validators
Clarity Act Defeat ‘Failure of American Leadership’: Trump’s Former Crypto Chief
William Shatner disowns QUATS token and calls charity pitch a scam
Helius CEO emphasizes Solana privacy features for institutional adoption
Latest articles


Latest coin listings on WEEX


