
Is There a Risk of Uncontrolled Access to Hyperliquid API Wallet Permissions? Itemized Permission Control May Be the Solution

 Prefer us on Google
The security boundaries of API wallets continue to degrade, and native permission control has become a critical shortcoming.
Written by: DevenMat, Co-founder of Valantis Labs
Compiled by: AididiaoJP, Foresight News
Note: The assumptions regarding the Hyperliquid state model in this article are primarily based on testnet transactions. The HyperCore state machine is currently a black box—nodes run signed binary files, and the code is not publicly available. The actual cost of implementing permission strategies for API wallets can only be estimated through testnet transactions and Hyperliquid's publicly disclosed architectural decisions. Until the node source code is made public, the community's ability to propose evidence-based improvements remains limited.
Hyperliquid, as a liquidity backend, enables individual agents to build a complete financial experience for users on a unified platform. It possesses deep liquidity, composability, programmability, and neutrality, positioning it as an irreplaceable financial infrastructure in the age of agents.
However, HyperCore currently lacks the core security capabilities that agents rely on—restricted permission policies. Permission policies are essentially limited permissions, such as allowing trades only in specified markets, requiring approval before opening positions, and prohibiting transfers to unknown addresses. It is these types of restricted permissions that enable today's non-financial personal agents to safely operate data such as emails, calendars, and contacts. Yet, over the past year, Hyperliquid has precisely removed support for such restricted API access.
The security boundaries of the API wallet (previously known as the agent wallet) have continuously degraded, reaching a point where it is no longer suitable to grant user account permissions to agents. It is important to emphasize that AI agents need to operate accounts on Hyperliquid through API wallets, but the current API wallet permissions are too broad and lack restrictions, making it highly risky to hand over the API wallet to AI agents.
This article attempts to find a path to re-establish Hyperliquid as a reliable financial backend for personal agents.
AI Agents in Wallets
AI agents are a key distribution channel for realizing Hyperliquid's vision of a "Liquidity AWS," allowing Hyperliquid to truly become the underlying layer of billions of people's daily financial lives.
The future of personal finance will involve agents directly accessing your portfolio and acting on your behalf with explicit authorization, calling upon funds, credentials, and data. If Hyperliquid is to become the financial layer for these agents, it must provide account-level permission control: allowing agents to access only specific parts of the account rather than the entire account.
The only feasible way currently is through CoreWriter, but latency issues render this solution incomplete, necessitating an additional layer of control at the native HyperCore level. The API wallet itself must also maintain a minimum security boundary to support the user experience required by agents.
Handing the API wallet directly to AI agents poses significant and ongoing risks.
Support for AI Agents Has Been Interrupted
The originally designed security boundaries of the API wallet have significantly degraded.
Now, as long as a user's account assets exceed approximately $40 million, if the API wallet is maliciously used, attackers can buy 500,000 HYPE with the account funds and stake them, subsequently launching a HIP-3 market controlled by themselves with these staked assets. As a result, the user's related assets will be locked for 183 days and face the risk of penalties. Moreover, this series of operations is irreversible; even if the user later revokes the API wallet, it cannot be undone.
The situation has not always been this way. Let’s review the historical boundaries.
In the initial design, the API wallet could not withdraw or transfer funds from the account.
However, the system never restricted the scale of margin that the API wallet could call. Once breached, attackers could transfer funds by placing malicious orders in illiquid markets (acting as the counterparty). In 2022, the API keys leaked from the trading bot service 3Commas were used to place orders in users' Binance accounts, specifically targeting the periods with the worst liquidity and easiest to manipulate.
In addition to the aforementioned attacks, a series of subsequent upgrades introduced new risk exposures that the original security architecture had not considered at all.
These unrelated upgrades accumulated, ultimately rendering the security boundaries of the API wallet virtually ineffective.
Risks
The API wallet has become the default way for users to trade on Hyperliquid through the interface. Currently, many wallets still directly list hosted API wallets in various builder code applications.
For ordinary trading applications, this risk may still be acceptable—after all, they only control a portion of the user base. However, once AI agents are introduced, the risks will escalate dramatically.
AI agents do not need to steal your API wallet private key to drain your account. They only need to be induced to read a piece of malicious text. Handing the API wallet to agents is equivalent to exposing all the aforementioned attack paths to anyone who can say a word in front of them.
Why Do API Wallet Permissions Continue to Expand?
Smart contracts on HyperEVM interact with HyperCore through CoreWriter, which is the foundational framework for Hyperliquid's programmable applications. Smart contracts can change HyperCore states in two ways: by calling CoreWriter actions or using the API wallet.
To enable smart contracts to have the same operational capabilities as ordinary accounts, the simplest approach is to continuously increase the permissions of the API wallet. The more ideal approach should be: whenever a new account operation that is sensitive to security but not to latency arises, a separate CoreWriter action should be added for it. However, maintaining CoreWriter is more costly—each new action requires an independent action ID, node-side support, and must appear as a separate transaction type on HyperCore. In contrast, directly increasing the permissions of the API wallet incurs very low costs while covering both smart contracts and ordinary accounts.
At the same time, almost all trading infrastructure on HyperCore adopts a similar architecture: low-latency API wallet hot keys deployed close to the network, while cold wallets are isolated offline. Therefore, all latency-sensitive operations must be executable by the API wallet to meet the needs of high-value accounts. This also explains why priority fee expenditures occur on the API wallet and why the staking deposits used to supplement priority fee balances were first included in the API wallet's permission scope—likely at the request of priority fee users.
The continuous expansion of API wallet permissions is due to different builders relying on it for various needs. The problem is that each upgrade indiscriminately expands external applications' control over user accounts, and users cannot opt out.
Permission Policies on Hyperliquid
Currently, the best way to implement action-based permission control on Hyperliquid is to use smart contract accounts on HyperEVM to control the corresponding HyperCore addresses. All HyperCore actions will first undergo custom Solidity checks before passing through CoreWriter. The Valantis Prime we developed is designed for this purpose: it leverages Obsidian's CoreWriterLib and custom Guardian to enable permission control and programmability for HyperCore transactions. Specific capabilities include:
- Setting different signers and thresholds for various actions in HyperCore multi-signatures;
- Setting whitelists and amount limits for HyperCore transfers.
However, this design completely fails in trading scenarios.
Transactions must be submitted through HyperEVM, undergo Solidity checks, and then wait for the next HyperCore block to process CoreWriter actions before they can truly execute. This approach is suitable for operations like staking, transferring, and lending that are not sensitive to latency, but it cannot meet the low-latency demands of trading.
To achieve low latency, the API wallet must interact directly with HyperCore, but the API wallet currently has no constraints or control layers.
Privy provides custodial services that can enforce policies before signing. We judge that if there are no native primitives to limit account signing permissions, custodial trusted signing middleware will become a key dependency for a large number of Hyperliquid users. We believe this is neither ideal nor necessary.
Relying on trusted middleware to implement the security primitives required for agents on Hyperliquid will undermine the fundamental reason agents should thrive here—directly connecting to trusted neutral liquidity infrastructure. Once AI agent applications must host private keys on servers, their room for development will be significantly reduced. For Hyperliquid in the next decade, implementing strategy layers natively on HyperCore is crucial.
Proposal: Add Permission Fields to API Wallets
Building a complete permission strategy layer for API wallets (including margin limits and market selection) may violate the design principle of HyperCore's minimal state. Therefore, we suggest adopting minimal action-level binary permissions.
The implementation should remain flexible and lightweight—using a bitmap to record whether each action type is allowed for API wallet calls or adopting an equivalent minimal structure.
Hyperliquid has already adopted a similar mechanism on HIP-3 deployers. Through setSubDeployers, deployers can grant or revoke permissions for other addresses to call specific perpDeploy variants on their DEX at any time—each action is authorized separately and limited to that action itself.
The same pattern can be applied to API wallets. During transactions, the system restores the signer, locates the main account, and checks the permission bits for the corresponding action type to determine whether the API wallet is authorized. The new state only requires a bitmap for each API wallet.
The core design principle is: when the network upgrades, API wallet permissions will not automatically expand.
Expected outcomes include:
API permission scopes can be safely expanded. Agents requiring relevant permissions can gain staking, withdrawal, and transfer capabilities without compromising the overall security architecture.
New L1 actions or network upgrades will no longer automatically expand the existing API wallet's permission scope. Actions can be added to the API wallet more freely without affecting overall security.
HyperCore accounts can achieve complete programmability without relying on custodial infrastructure. When CoreWriter is combined with constrained API wallets, each action can be configured with custom security rules without causing state bloat for HyperCore.
The core advantage of blockchain lies in its composability and programmability. Hyperliquid, in its early pursuit of performance, actively reduced programmability. The introduction of HyperEVM and CoreWriter is precisely to supplement HyperCore's programmability with lower resource overhead.
The lack of a native, minimal control layer for API wallets means that this capability is still incomplete.
This content is provided for general informational purposes only and doesn't constitute financial, investment, legal, or tax advice. Any events, rewards, online promotions, or related information mentioned herein should not be considered a recommendation, solicitation, or invitation to purchase, sell, trade, or otherwise deal in any crypto assets. Crypto assets are highly volatile and may result in loss. The availability of WEEX services, products, and related events may vary by region. You are responsible for ensuring that your participation is in accordance with applicable local laws and regulations.
You may also like

Disney Aims for $3 Billion Annual Cost Savings by Fiscal Year 2029

Home Depot Appoints Richard McPhail as New CEO, Q3 Performance Exceeds Expectations

CoinGecko Acquired: Two People Started with $200, Once Valued at $500 Million

Trump Media Creditors Can Claim $1 Billion on November 30

Hong Kong-listed firm sells 300 Bitcoin for $19.2M to fund AI deal

Dubai Airport Sees Decline in Passenger Traffic Due to Iranian Conflict, but Signs of Recovery Emerge
Micron Has Plunged 36% From Its Peak. Here’s the Price at Which I’d Buy.

stUSDT Begins Wind-Down as JustLend Plans to Remove Its Wrapped Token Market

Prediction: The Stock Market Will Make a Big Move on Nov. 18 (Hint: Nvidia Will Be the Catalyst)

Controversial AI Explainability Research Draws Attention from Sam Altman

Does an AI Trading Tool Need Permission to Place Orders on WEEX?

Why Is Bitcoin Falling? BTC Near $64K as Anthropic IPO Looms

Tether-backed Twenty One Capital buys $10M in Bitcoin as stock slides

The Next Hyperliquid Will Emerge from These 6 Companies

A $25 million MEV ruling exposes a dangerous blind spot in Wall Street’s tokenization push
A Super Empire on a Fragile Foundation: How Jensen Huang Has Controlled NVIDIA for 33 Years
Binance’s He Yi explains AI Pro transfers after hack-day withdrawal claims

Q3 Institutional Holdings Observation: Large-Cap Tech Underweight Narrowing, Funds Concentrating on AI Infrastructure, Software Stocks Neglected

Microsoft Ignite Conference Kicks Off Today! Focus on Copilot Monetization and AI Computing Returns, Can the Enterprise AI Flywheel Deliver?

How to Reassess Core Assets with 'Revenue + Narrative' After Market Crash?
Circle Expands Disparte and Walia Roles as Stablecoin Operations Scale
US Deploys Third Aircraft Carrier to the Middle East as Iran Intensifies Threats Amid Tanker Attack in the Strait of Hormuz

Wall Street Sees 'Gazumping' Phenomenon as Hedge Funds Compete for Top Talent
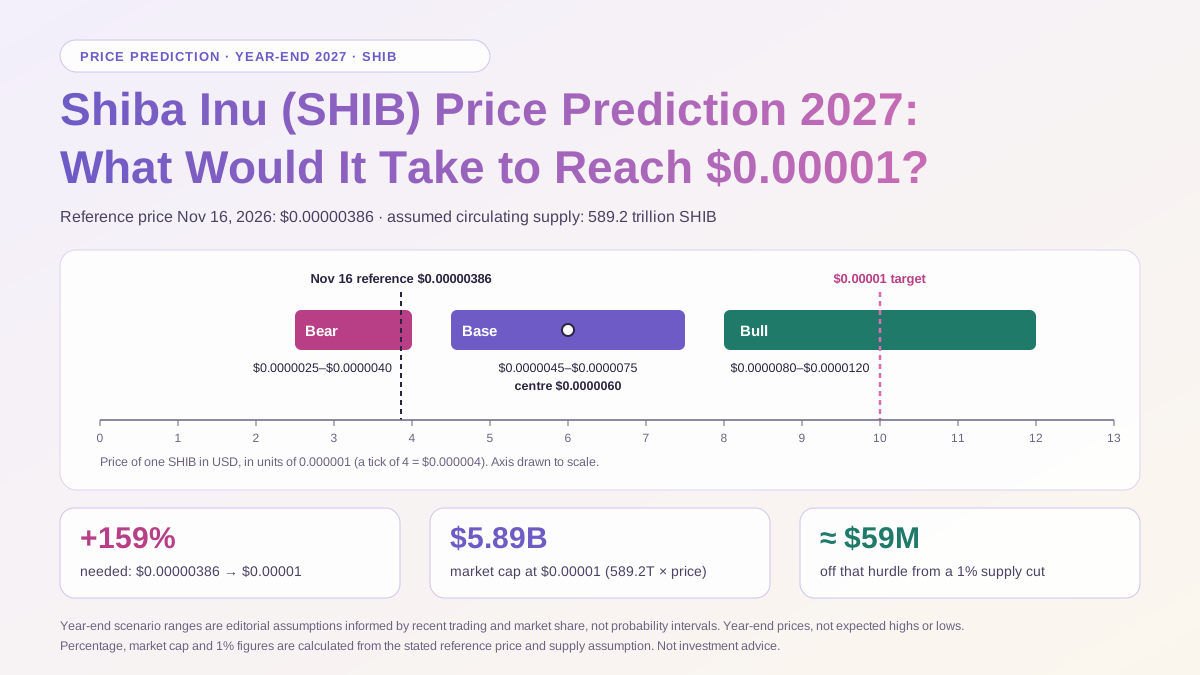
Shiba Inu (SHIB) Price Prediction 2027: What Would It Take to Reach $0.00001?
See our Shiba Inu price prediction for 2027, including the $0.000006 base estimate, the market cap needed for $0.00001, and how much burns could help.

Huya's Q3 2026 Financial Report: Operating Profit Turns Positive for the First Time in Nearly Four Years, Live Streaming and Game-Related Services Continue to Improve Efficiency

Aave Labs Reports: A 97-Person Team Supporting What Kind of DeFi Business?

Prediction: Anthropic Will Have a Successful IPO but Then the Stock Will Trade Like SpaceX

Intesa Sanpaolo raises XRP and Solana ETF holdings, cuts Bitcoin and Ethereum

Why Are Tokenized Stocks Seeing Strong Buying Pressure While Prices Keep Falling?

Report: Israel Uploads Millions of Photos to Amazon's Facial Recognition Platform to Track Palestinians
Disney Aims for $3 Billion Annual Cost Savings by Fiscal Year 2029
Home Depot Appoints Richard McPhail as New CEO, Q3 Performance Exceeds Expectations
CoinGecko Acquired: Two People Started with $200, Once Valued at $500 Million
Trump Media Creditors Can Claim $1 Billion on November 30
Hong Kong-listed firm sells 300 Bitcoin for $19.2M to fund AI deal
Dubai Airport Sees Decline in Passenger Traffic Due to Iranian Conflict, but Signs of Recovery Emerge
Latest articles


Latest coin listings on WEEX


